Continu-US · Continuous control verification
Your baseline, verified daily.
Continu-US proves every day that your environment still meets your own baseline, the one your SSP commits you to and your assessor tests against, not only at assessment time.
Continuous control verification for defense contractors and government, built by an assessor-led firm. Use it to build, run and monitor a compliant environment, with evidence ready whenever you need it.
Already an ATLLC managed security client? Continu-US is included in your service.
Daily
Endpoint checks against your baseline
320
CMMC Level 2 assessment objectives mapped
3
Frameworks mapped today, and customizable
Your tenant
Runs in your own Azure, Commercial or Government
Assessor-led, independent
Built to support your compliance program, not to certify it
Continu-US supports your compliance program; it doesn’t certify it, and it doesn’t guarantee an assessment result. It shows you where you stand every day, so you can fix drift long before an assessment.
We never assess an organization we manage, advise, or license Continu-US to.
How it works
From your baseline to daily evidence
01
Connect
Install Continu-US in your own Azure tenant, then connect your endpoints, cloud accounts, network devices, ticketing system and SIEM.
02
Set your baseline
Bring your own baseline from your GPO exports, STIG checklists, SCAP results or a custom baseline, and set your own required values, such as your lock-screen timeout, without changing scripts.
03
Verify daily
Every Windows and Linux endpoint is checked daily against your baseline, and everything else on the cadence you set. Drift shows up close to real time.
04
Export evidence
Hand your assessor an evidence package, run quarterly reports and send branded status reports whenever you need them.
Capabilities
What Continu-US does today
Endpoints
- Checks every Windows and Linux endpoint daily against your own baseline and shows what drifted
- Bring your own baseline: built from your GPO exports, STIG checklists, SCAP results or a custom baseline
- STIG and GPO compliance reports, with every result traceable to the STIG or GPO it came from
- Set your own required values for checks without changing scripts
Cloud
- Configuration checks for Microsoft 365, Entra, Intune and Azure
- Configuration checks for AWS, Google Cloud and Google Workspace
- Connect accounts directly with no scripts, or upload results
Network & tools
- Firewall configuration checks, with switch and router support on the way
- Connects to your ticketing system for change evidence
- Connects to your SIEM for alert evidence
Frameworks & evidence
- Maps to NIST SP 800-171A: all 320 CMMC Level 2 assessment objectives
- Maps to NIST SP 800-53 Rev 5 (800-53A) and PCI DSS 4.0.1, and can be customized to other frameworks
- Recurring compliance activities with screenshot evidence
- Policy and procedure documents mapped to objectives
- POA&M tracking with export
- Assessor-ready evidence packages, quarterly reports and branded status reports
- Evidence close to real time, on a cadence you set: daily, weekly or whatever you need
Your tenant, your data
- Runs inside your own Azure tenant, Commercial or Government, as a managed application, so your data never leaves your tenant
- You choose supported access or no vendor access at all
- Signed automatic updates and a software bill of materials with every release
- A published vulnerability disclosure policy
- One install can monitor many organizations, for MSSPs and for primes monitoring their suppliers
On the roadmap: more integrations (MFA, EDR and vulnerability scanners) and AI-assisted drafting of implementation statements.
See it
Inside Continu-US
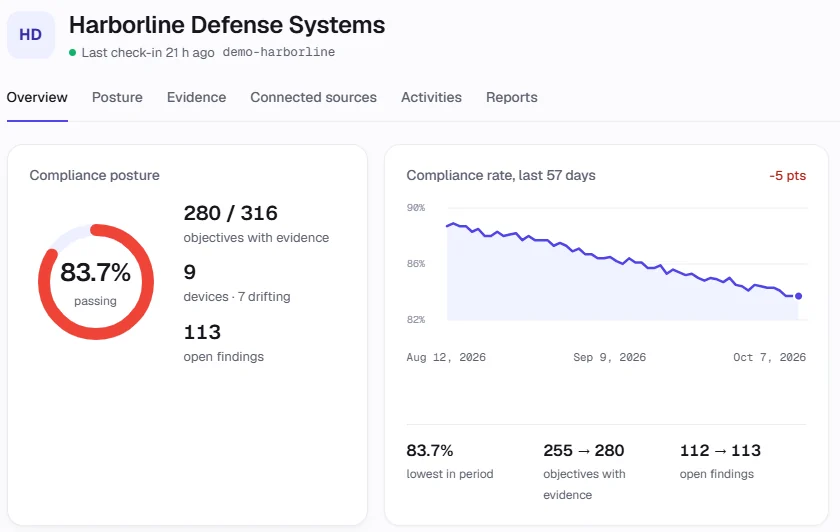
Daily posture and trend
Posture, drift and open findings, with the trend over time.
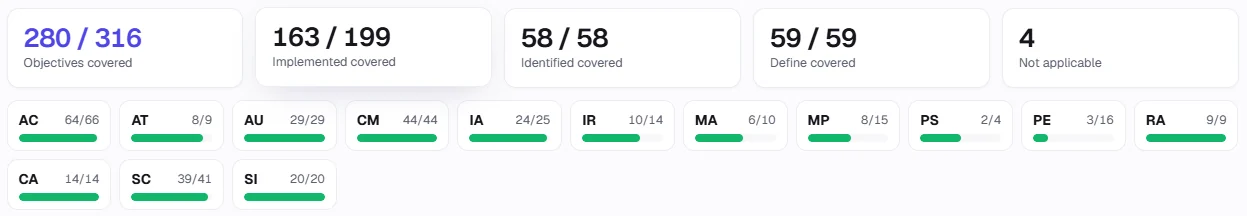
Every objective, every family
Coverage for every objective, family by family.
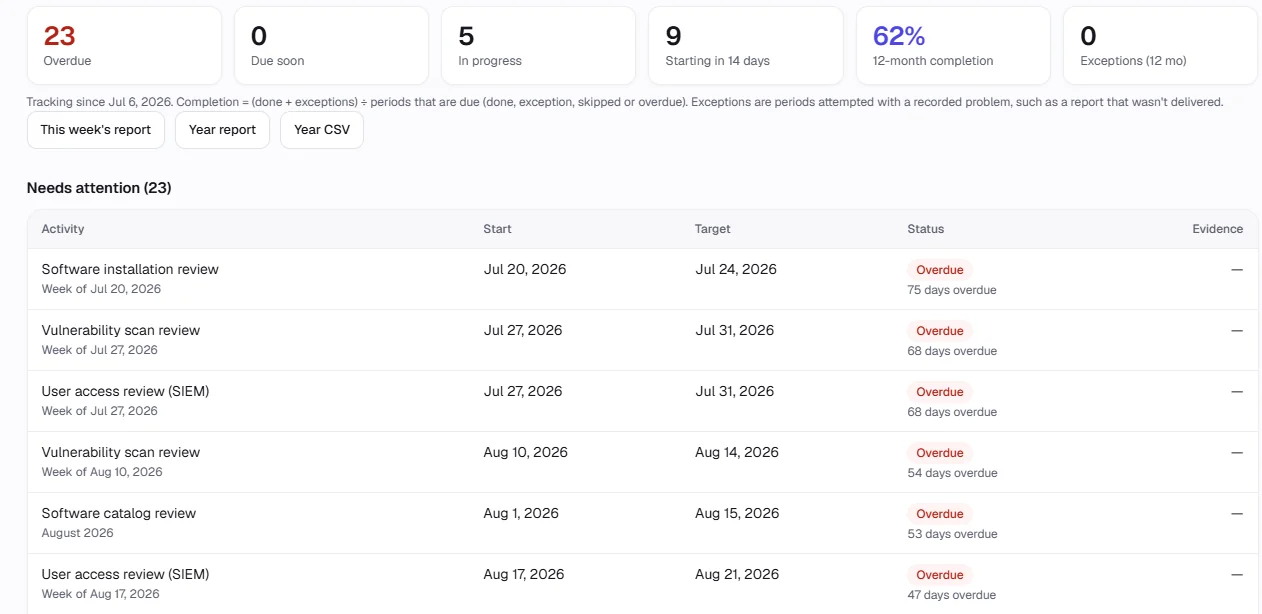
Recurring activities
Recurring compliance activities, with evidence attached.
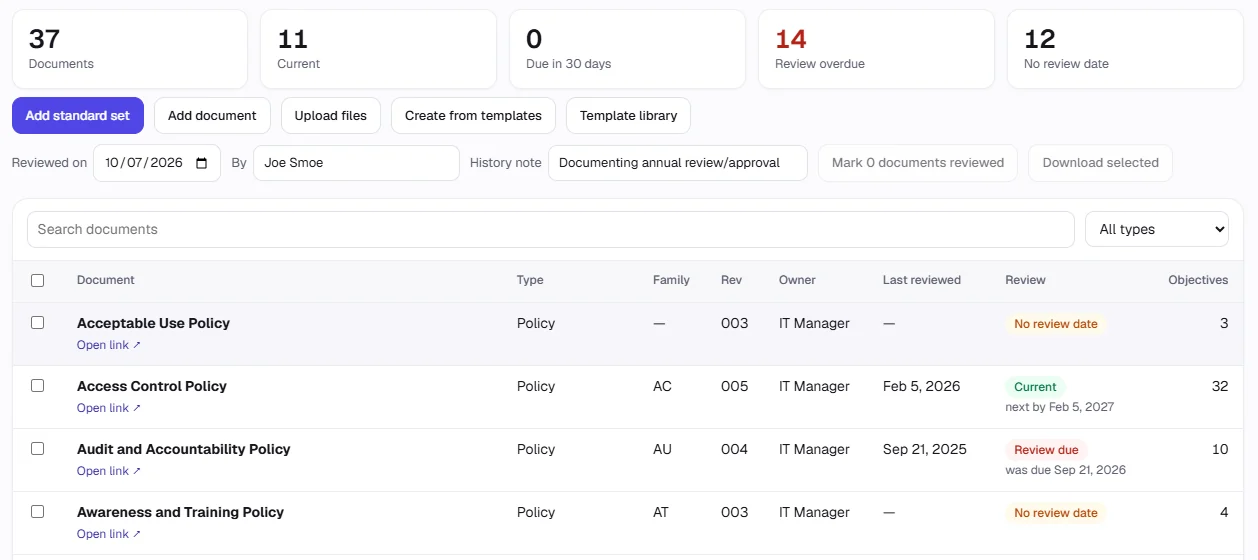
Policies and procedures
Policies and procedures mapped to the objectives they support.
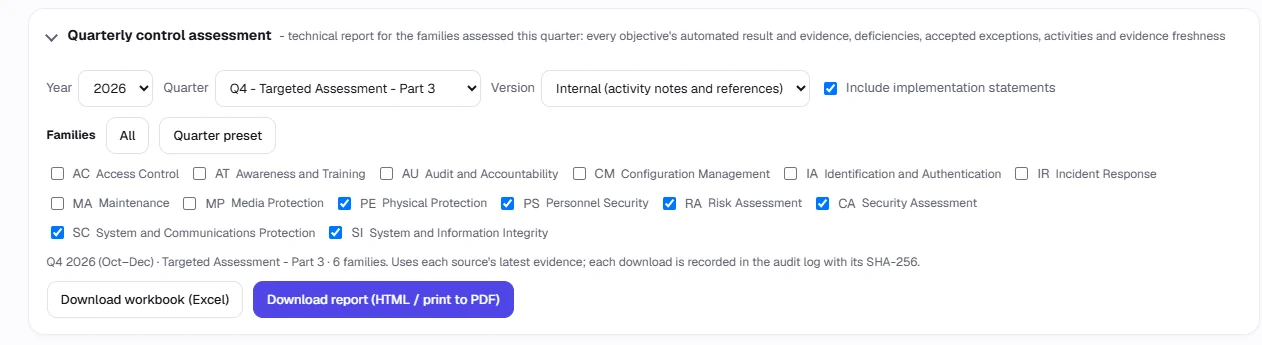
Quarterly reports
Pick the quarter and the control families to report on.
Built by assessors
Built by the people who do the assessments
Continu-US comes from Anthony Timbers LLC, an authorized CMMC Third-Party Assessment Organization (C3PAO) whose assessments are led by Certified CMMC Assessors (CCAs) and Lead CCAs. We built it to check what assessors check, the way they check it, so the evidence holds up when it matters.
We’re also a CMMC Level 2 certified MSSP, a FedRAMP 3PAO and a PCI QSA.
Who it’s for
Built for the defense industrial base and government
Small and mid-size defense contractors
Keep your self-assessments, SPRS score and annual affirmations backed by current evidence, and be ready when your contracts or primes call for certification.
Government
Programs working under RMF and NIST SP 800-53 get continuous, objective-by-objective evidence instead of a once-a-year snapshot.
Primes
Monitor your suppliers’ compliance from one install, with each supplier kept separate.
MSSPs
One install for all of your clients, with endpoints pooled across them. See the MSSP partner program.
See your own baseline verified
Book a demo and we’ll walk through Continu-US against the kind of baseline you already have: GPOs, STIGs, SCAP results or your own standard.
Security: read our vulnerability disclosure policy. Continu-US supports your compliance program; it doesn’t certify it, and it doesn’t guarantee an assessment result.
Get a quote
Tell us roughly how many endpoints, network devices and cloud accounts you’d connect, and we’ll send a quote. Prefer to see it first? Book a demo.
One firm. Four authorizations.
MSSP
CMMC Level 2 Certified MSSP
24/7 security monitoring and incident response for small to mid-sized businesses and DoD contractors.
C3PAO
Authorized CMMC C3PAO
Official CMMC Level 2 certification assessments, authorized by the Cyber AB.
3PAO
FedRAMP 3PAO
FedRAMP Rev5 and 20x assessments as a FedRAMP Recognized independent assessor, accredited to ISO/IEC 17020.
QSA
PCI Qualified Security Assessors
PCI DSS assessments and consulting, listed as QSAs on the PCI SSC website.
Team credentials
ISO/IEC 17020 accredited